Vue I18n XSS: escapeParameter misses srcdoc, update to 11.4.14
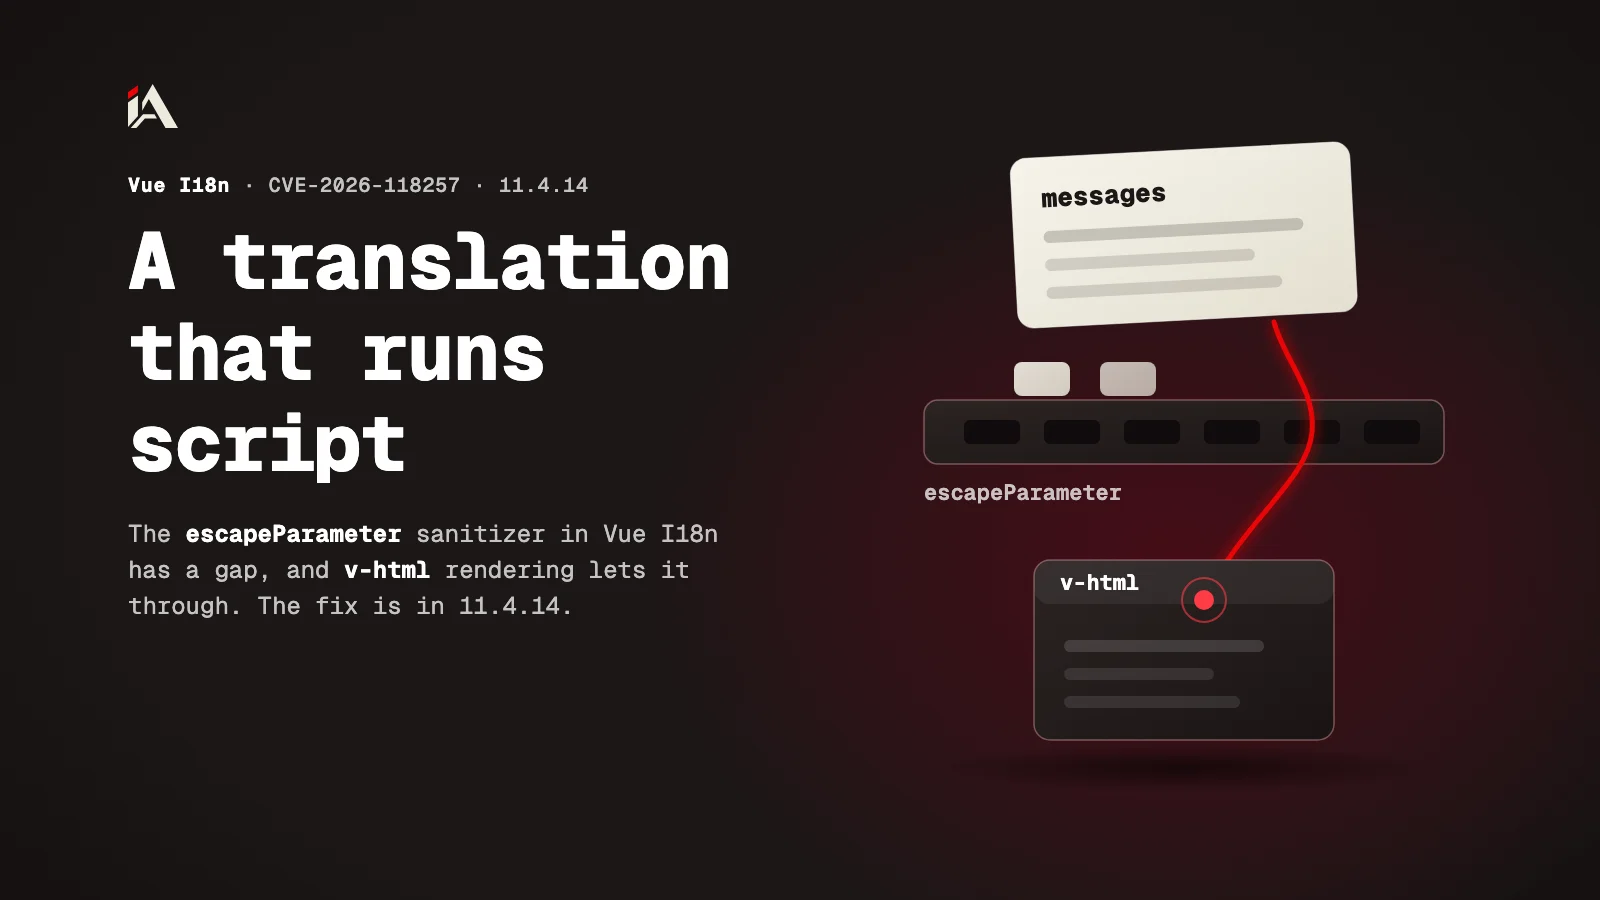
Vue I18n with escapeParameter sanitizes translations but does not handle the iframe srcdoc attribute, so a translation rendered with v-html can run script on your site. The fix is in 11.4.14.
If your Vue site renders Vue I18n translations as HTML, there is an XSS flaw that gets past the sanitizing you think protects you. Here is how to tell whether your app is affected, and how to fix it.
What is the Vue I18n flaw?
The Vue I18n flaw is that the escapeParameter option sanitizes translations, escaping angle brackets and neutralizing event handlers, but does not handle the srcdoc attribute of <iframe>. So a translation with srcdoc in it can run script on your page.
XSS is when an attacker runs their own JavaScript inside your site, with the same rights as your page.
The advisory in the GitHub Advisory Database is GHSA-83rm-6c8r-g728, and the flaw is CVE-2026-118257. It is rated high: 7.2 on CVSS 3.1.
Why does srcdoc get past the sanitizer?
The reason is that the browser decodes character references inside srcdoc, then parses the result as a full nested document inside the iframe, with the same origin as your site. So the brackets the sanitizer escaped turn back into real brackets there.
The advisory says this flaw bypasses the fix for an earlier one, CVE-2025-53892, which is the fix that added the sanitizer in the first place.
Is my app affected?
Your app is affected if all of these are true:
Your version is an affected one: from 11.1.10 up to before 11.4.14, or 9.14.5, 10.0.8 or 12.0.0-alpha.4.
escapeParameteris enabled (orescapeParameterHtmlin the Legacy API).You render the translation as HTML, for example with
v-html.Something in the translation comes from a source you do not trust: a user value placed inside
srcdoc, or message text that is partly not yours, such as crowdsourced translations.
The affected packages are vue-i18n, petite-vue-i18n and the @intlify packages under them.
Our articles about site front ends and their libraries are in one place: Web development.
How do you fix it?
Update vue-i18n to 11.4.14, or to 12.0.0-alpha.5 if you are on the 12 pre-release. The fix makes the sanitizer handle srcdoc the way it already handles event handlers.
npm ls vue-i18n
npm install vue-i18n@11.4.14
If you are on v9 or v10, there is no fix: the advisory says they are no longer supported, and recommends moving to v11.
Until you update, the advisory gives two workarounds:
Render translations that may contain outside content with
<i18n-t>instead ofv-html. Rendering through<i18n-t>is not affected, because it does not render translations as HTML.Do not put
srcdocin translation messages, and do not pass values into it.
Where do you start now?
Start with your version and the places where you render translations as HTML.
Run
npm ls vue-i18nand check whether your version is an affected one.Search your code for
v-htmlnext to$tort(, and forescapeParameter.Update to 11.4.14, and swap
v-htmlfor<i18n-t>where the translation carries user values.
If you want someone to look for XSS in your site's front end the way an attacker would, that is what Muhassan does.
All our app security articles are in one place: App security.
FAQ
I am on Vue I18n 9 or 10. Is there a fix for me?
No. The advisory says v9 and v10 are no longer supported and will not be fixed, and the way out is moving to v11.
If I render translations with i18n-t, am I affected?
No. The advisory says rendering through i18n-t is not affected, because it does not render translations as HTML.
Why a new flaw if escapeParameter was fixed before?
Because this flaw bypasses the fix made for CVE-2025-53892. That fix did not handle srcdoc.